
Formidable includes several built-in options for spam protection, including a captcha and captcha alternatives. Each spam check either rejects a suspicious submission with an error message or saves it as a spam entry that you can review later.

Upgrade your WordPress site with powerful, flexible forms.
Spam form settings
To access the spam settings for a particular form, open the form and click Settings at the top of the form builder (1). Then click Spam in the left menu (2). The checks that apply to every form are listed under Global Spam Settings and are managed in the global settings. Until a captcha service is set up, the Include Captcha in this form box is grayed out. Until then, a notice links to the global spam settings.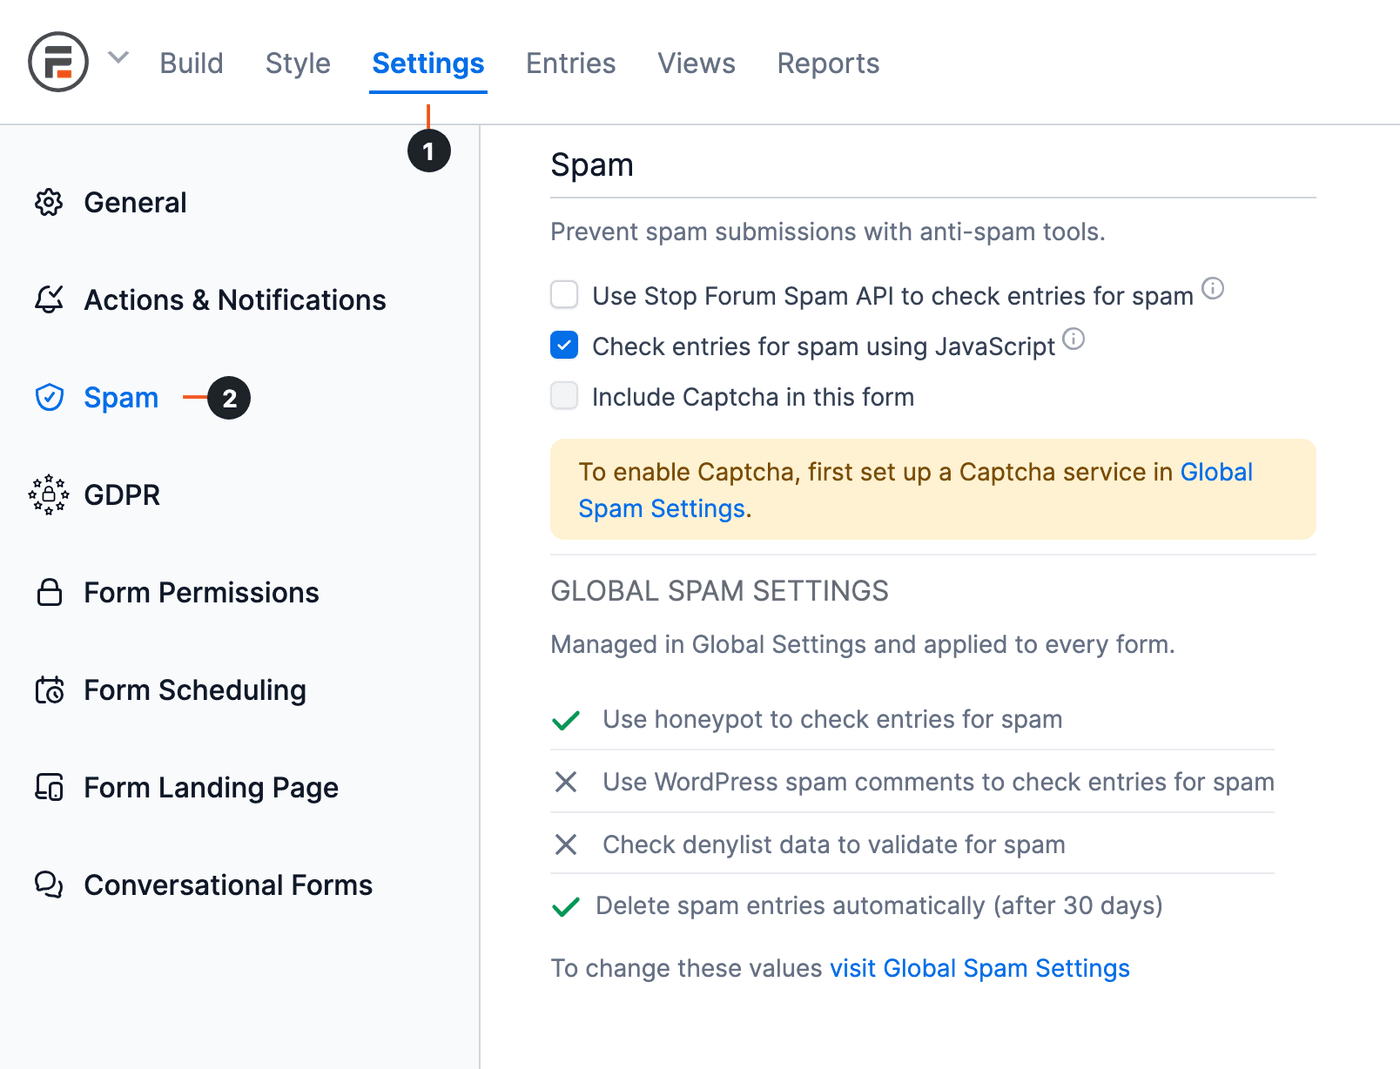
From Idea to Reality in Minutes. Build Powerful Forms, Dashboards, Apps and More.
Formidable Forms makes advanced site building simple. Launch forms, directories, dashboards, and custom WordPress apps faster than ever before.
Which options should I use?
Formidable's spam options work in layers, and each catches something different. We recommend enabling them in this order and stopping once spam stops:
| # | Option | Where | Catches | Default handling |
|---|---|---|---|---|
| 1 | Check entries for spam using JavaScript | Form → Spam | Bots that don't run JavaScript | Reject |
| 2 | Honeypot | Global → Captcha/Spam | Bots that fill hidden fields | Reject |
| 3 | Turnstile / reCAPTCHA / hCaptcha | Global + Form | Bots and scripted submissions | Reject |
| 4 | Use Stop Forum Spam API | Form → Spam | Known spam IPs and email addresses | Save as spam |
| 5 | Denylist | Global → Captcha/Spam | Spam keywords in text content | Save as spam |
| 6 | Use Akismet | Form → Spam (Akismet active) | Broad spam patterns | Save as spam (blatant spam: Reject) |
| 7 | WordPress spam comments | Global → Captcha/Spam | IP addresses, emails, and websites from recent spam comments | Save as spam |
Choose what happens to spam
Each spam check can either reject a flagged submission or save it as a spam entry. Checks that catch bots reject by default, because bots can send many submissions. Checks that look at the content save by default, so you can recover a real message that was flagged by mistake.
- Go to Formidable → Global Settings → Captcha/Spam.
- Under Spam checks, click Customize how spam submissions are handled to open the list of checks.

- For each check, choose what happens when it flags a new submission:
- Save as a spam entry: The entry is saved to the Spam tab of the entries list. Form actions such as email notifications don't run, and the submitter sees the normal success message.
- Reject with an error message: The submission isn't saved, and the submitter sees a spam error message.
- Click Update to save your changes.
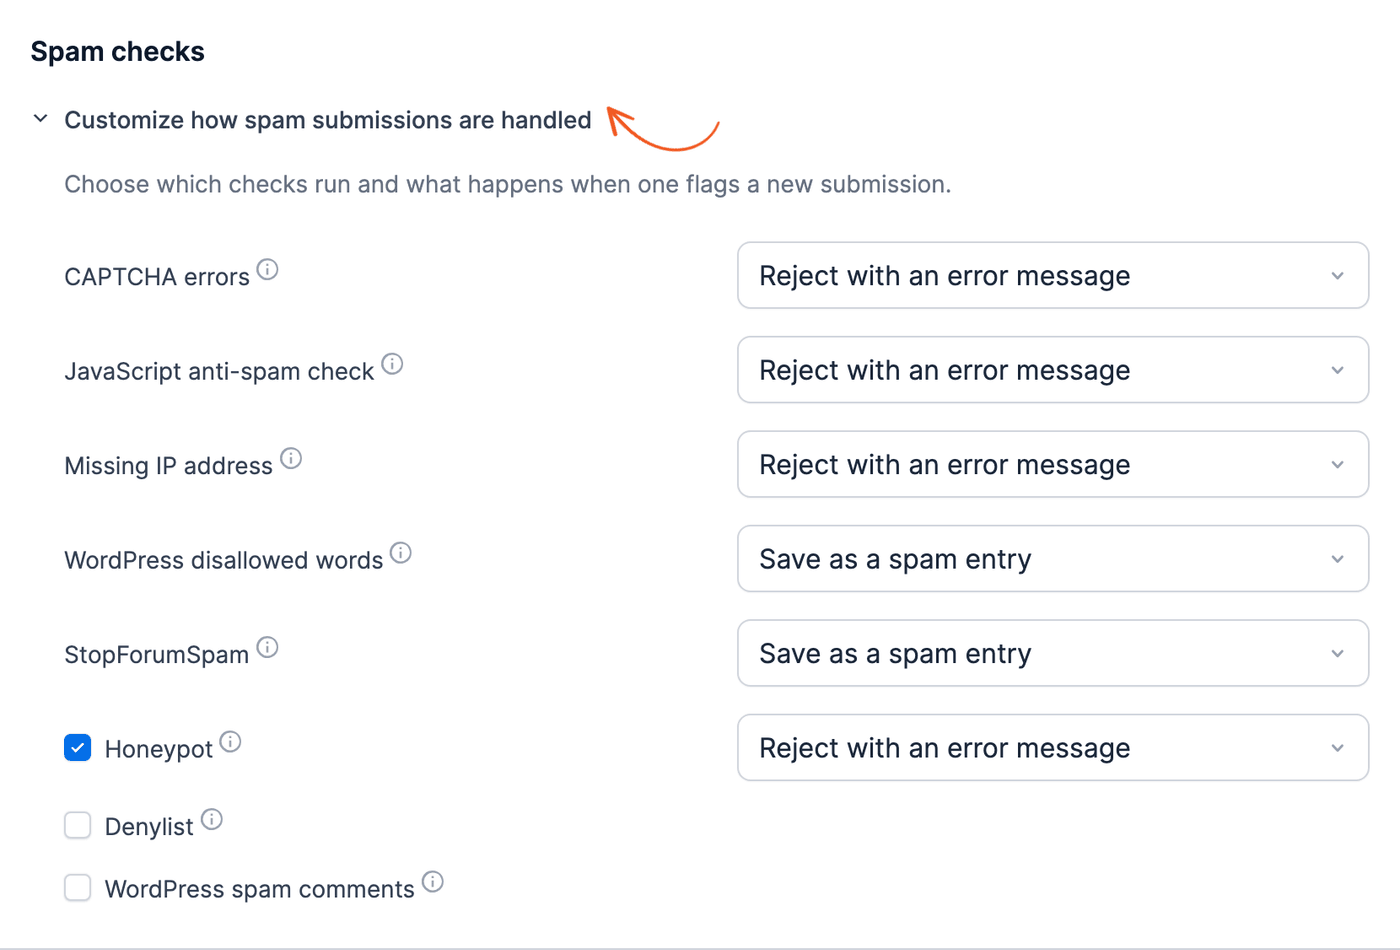
The list includes these checks:
- CAPTCHA errors: A reCAPTCHA, hCaptcha, or Turnstile check failed. Reject by default. A saved spam entry includes the captcha error details.
- JavaScript anti-spam check: The submission failed the JavaScript token check, such as a bot that doesn't run JavaScript. Reject by default.
- Missing IP address: The submitter's IP address couldn't be detected. Reject by default.
- Akismet spam and Akismet blatant spam: Only shown when the Akismet plugin is active. Akismet spam is saved by default, and blatant spam (spam Akismet recommends discarding) is rejected by default.
- WordPress disallowed words: The submission matches the Disallowed Comment Keys in Settings → Discussion. Save by default.
- StopForumSpam: The IP address or email address is flagged by the StopForumSpam service. Save by default.
- Honeypot, Denylist, and WordPress spam comments: These checks can be turned off. Check the box to run the check, then choose how to handle it. Honeypot rejects by default, and the other two save by default.
Only new submissions are saved as spam entries. When an existing entry is edited, a flagged change still shows the spam error.
JavaScript token
Use this for more effective spam protection using JavaScript, including protecting file uploads from spam. This spam option generates a token that is specific to your site, and is good for at least 24 hours.
To turn on the JavaScript token, go to the form's Settings → Spam tab and check the box to Check entries for spam using JavaScript.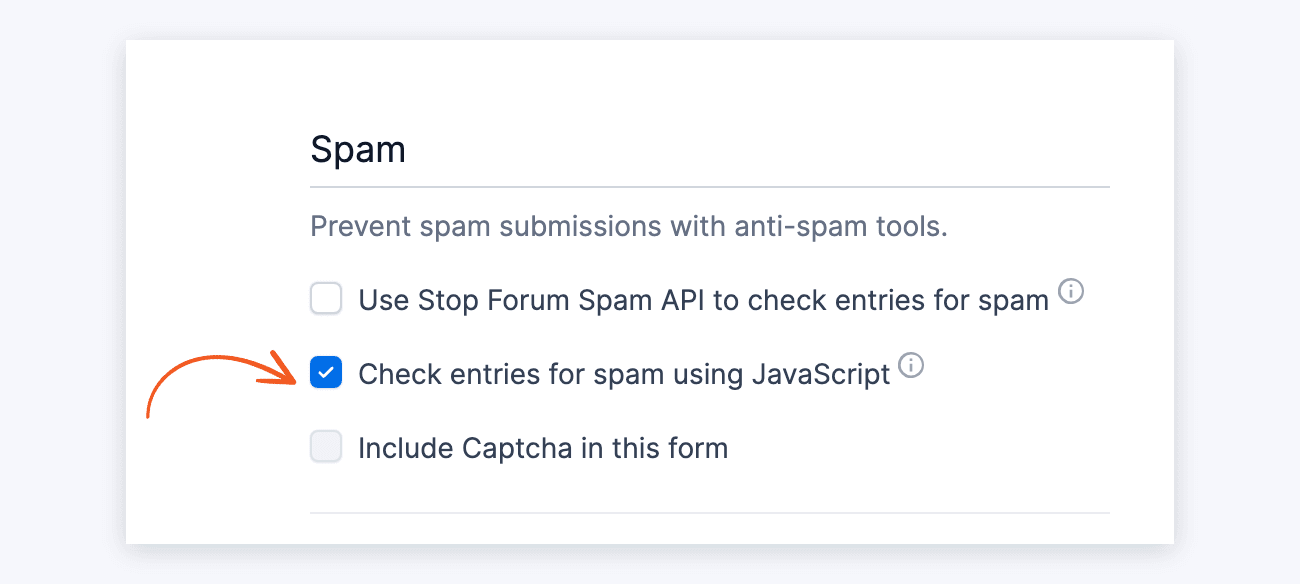
With this option enabled, the token may be cached longer than expected and end up with false positives. If you run into this, you can increase the expiration time on the token with custom code. To save a flagged submission for review instead, set the JavaScript anti-spam check to Save as a spam entry in the spam checks.
If you need to extend the valid token times before or after today, use the frm_form_token_check_before_today or frm_form_token_check_after_today hook.
Stop Forum Spam API
Go to the form's Settings → Spam tab. Select the Use Stop Forum Spam API to check entries for spam checkbox to validate form entries for spam against the StopForumSpam API. When this is enabled, IPs and email addresses will be validated against a spam database.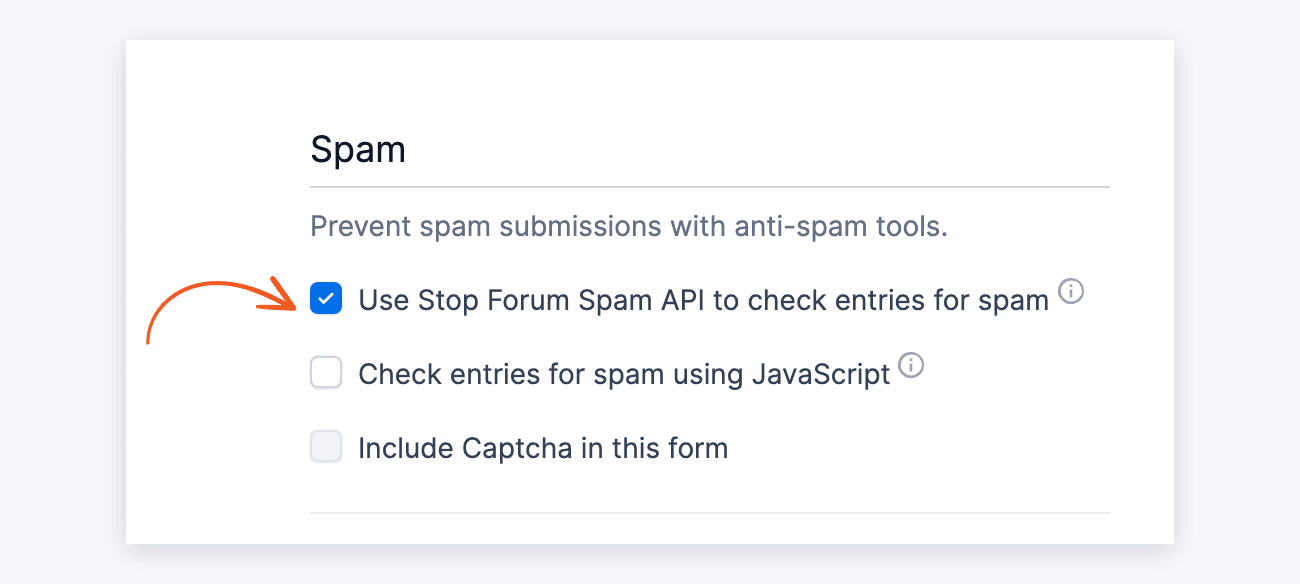
Honeypot
Honeypot is a type of invisible spam protection. Normal users won't be affected by this spam protection. A submission that fills in the hidden honeypot field is flagged as spam and rejected with an error message by default.
Honeypot is on by default and applies to all forms. To change it, go to Formidable → Global Settings → Captcha/Spam and open Customize how spam submissions are handled. Uncheck Honeypot to turn it off, or choose how flagged submissions are handled in its dropdown.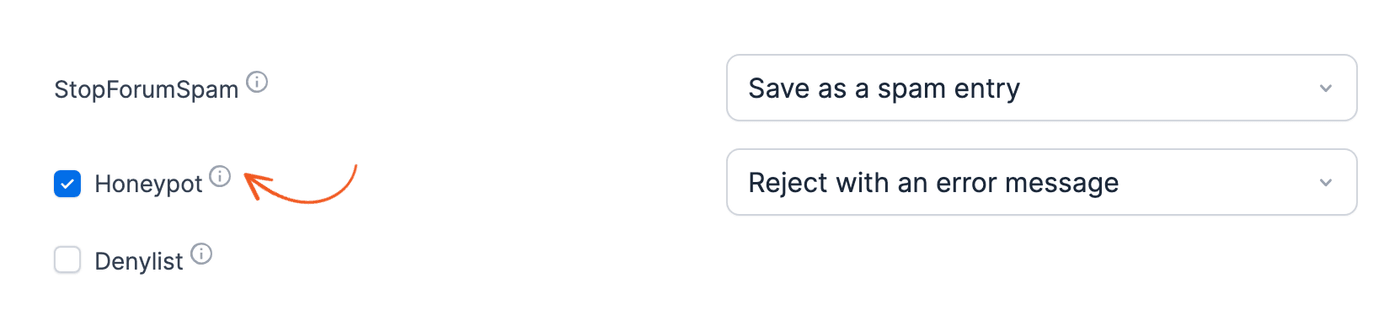
Empty field above form
If the Formidable styling is missing from the page, you may see the empty form field at the top of each form. If you see this extra field with the label 'If you are human leave this field blank', try these fixes:
- Clear any caching from your site (from a plugin, or from your host), and then refresh the page.
- If the issue persists, go to the Form Styler page and click the Update button.
Check Denylist Data
The denylist check looks for common spam words in text and paragraph fields (as well as custom "Other" options in checkbox and radio button fields).
- Go to Formidable → Global Settings → Captcha/Spam and open Customize how spam submissions are handled.
- Check the Denylist box. By default, a submission that contains a denylist word is saved as a spam entry.
- To add your own words, click Customize denylist words. Enter one word or phrase per line in Custom disallowed words.
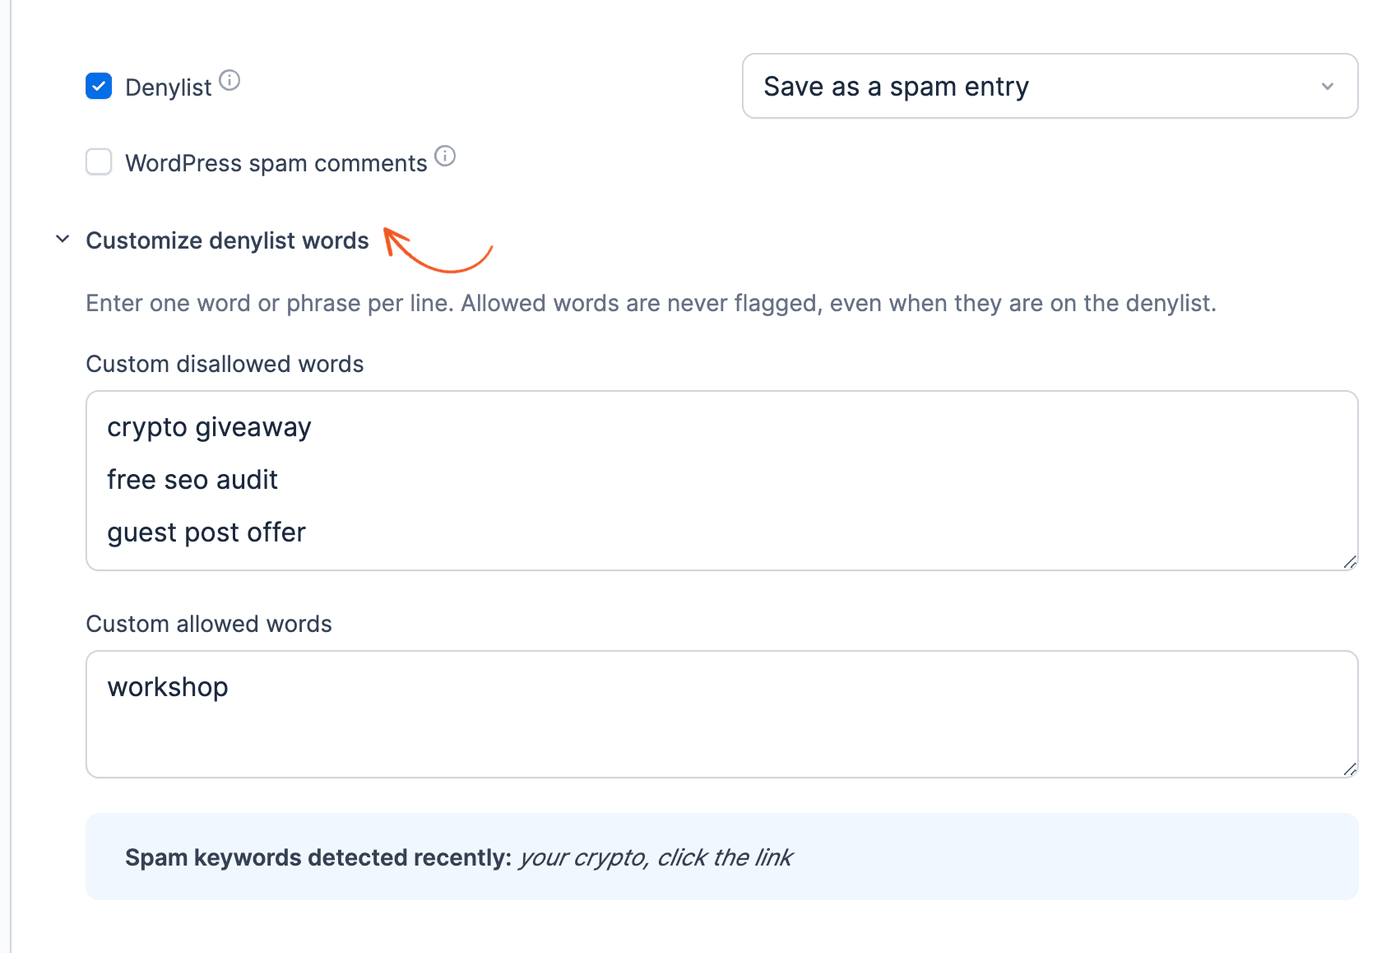
Custom allowed words create exceptions. They apply to Formidable's denylist and to your WordPress Disallowed Comment Keys.
Formidable's denylist contains thousands of terms and isn't published. When something is flagged, the detected words appear under Spam keywords detected recently, below Custom allowed words. Copy them into Custom allowed words if the spam protections are too strict.
Akismet
Akismet saves you time by automatically detecting spam. It runs hundreds of tests on each entry and determines whether it's spam. By default, entries Akismet flags are saved to the Spam tab for review, and blatant spam is rejected. Set it up with these steps:
- Go to your WordPress plugins. Install and activate Akismet.
- Sign up for an Akismet API key. Akismet may require a paid subscription depending on the type of site you have.
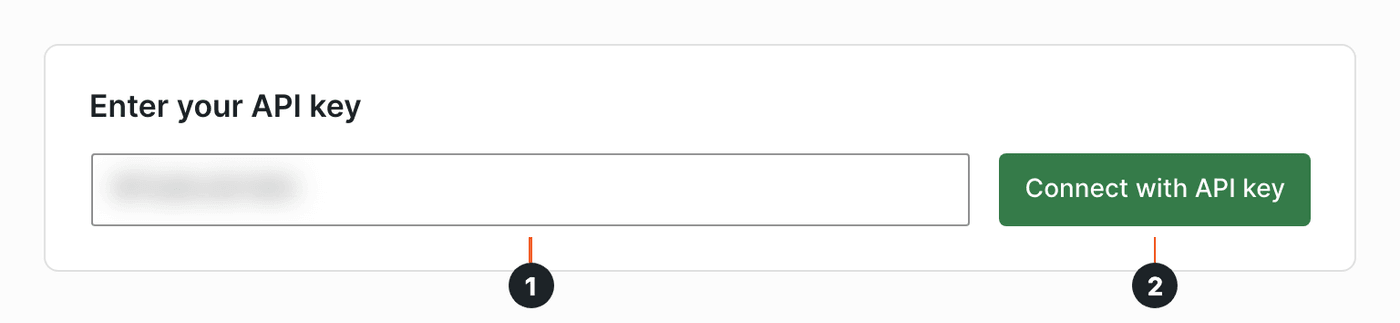
- Go to Settings → Akismet Anti-spam. This page also opens right after you activate Akismet. Click Manually enter an API key. Paste your key (1). Then click Connect with API key (2). Akismet shows "Akismet is now protecting your site from spam."
- Go to the form Settings page for each form you want to protect. Click the Spam tab to find the Use Akismet to check entries for spam for dropdown.
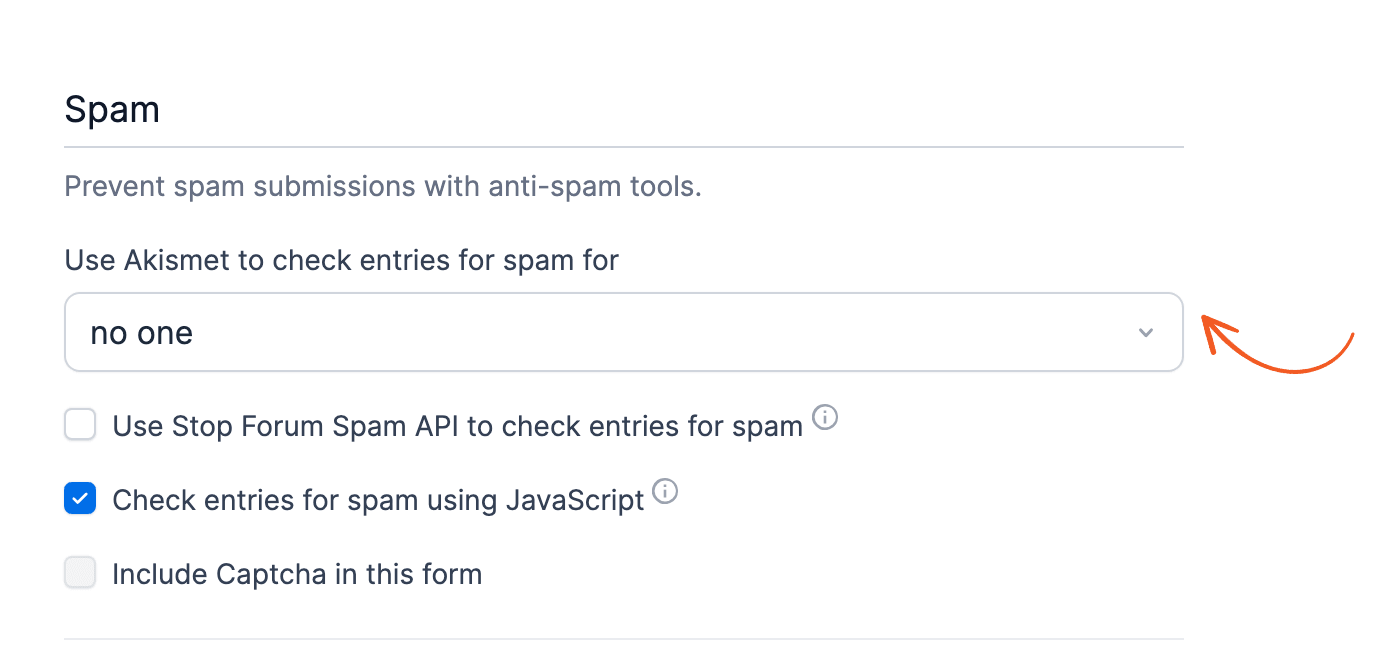
You can set Akismet to check entries for no one, everyone, or visitors who are not logged in. Once Akismet is active, the Akismet spam and Akismet blatant spam checks also appear in the spam checks.
Akismet Troubleshooting
On a local test site, Akismet can flag every entry as spam, even a normal message. Test Akismet on your live site. To recover an entry flagged by mistake, mark it as not spam.
If you are seeing an error message like Your entry appears to be spam, you might have an email address or URL that is getting flagged. Please contact Akismet support. Choose the I think Akismet is catching my comments by mistake option, and they'll investigate the issue.
Captcha
Captchas are used by many websites to prevent abuse from 'bots', or automated programs usually written to generate spam. Bots cannot easily submit forms protected by Captcha.
A failed captcha is rejected by default. To save it as a spam entry instead, change the CAPTCHA errors check in the spam checks.
reCAPTCHA
reCAPTCHA is a script that judges whether a user is a human or a robot. You have probably seen some variation of reCAPTCHA.
Learn more about setting up reCAPTCHA in your forms.
hCaptcha
hCaptcha is a program that is designed to distinguish human users from spam via a challenge-response test. It is a popular alternative to Google's reCAPTCHA.
Learn more about setting up hCaptcha in your forms.
Turnstile
Turnstile by Cloudflare is an alternative to CAPTCHAs that is available at no cost. This solution helps reduce spam form entries without sacrificing user experience or compromising visitors' data privacy. It provides your website visitors with a seamless, hassle-free experience while verifying their authenticity.
Learn more about setting up Cloudflare Turnstile in your forms.
Comment Blacklist
In addition to Honeypot spam protection, every form submission is checked against the Disallowed Comment Keys in your WordPress discussion settings. This is the WordPress disallowed words check. It lets you add custom terms to the comment blacklist and integrate several spam protection plugins without extra effort.
To add words, IPs, or URLs to your blacklist, go to the WordPress Settings → Discussion page. Add values in the Disallowed Comment Keys box, following the WordPress instructions: One word or IP address per line. It will match inside words, so "press" will match "WordPress."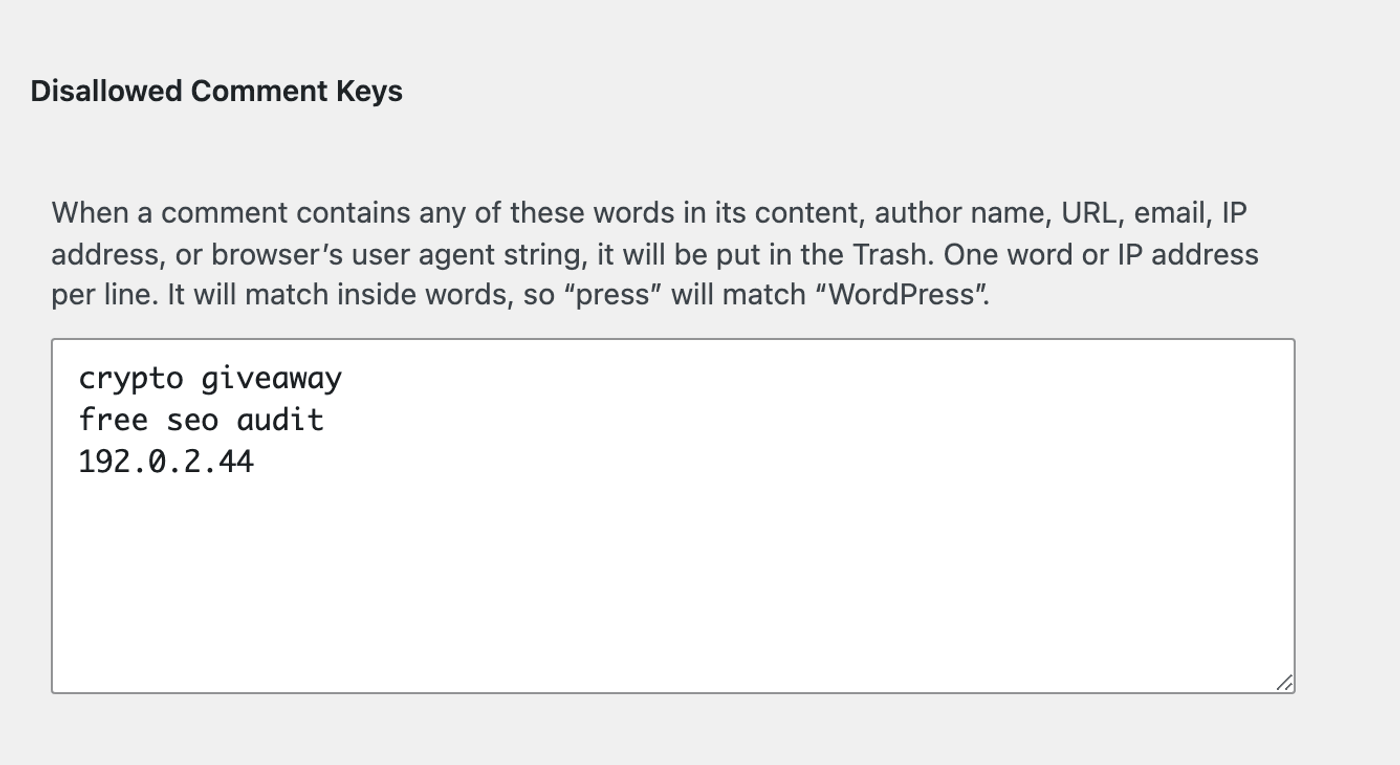
You can also check entries against recent comments that WordPress marked as spam. In Formidable → Global Settings → Captcha/Spam, open Customize how spam submissions are handled and check WordPress spam comments. This check matches the submitter's IP address, email, or website against recent spam comments.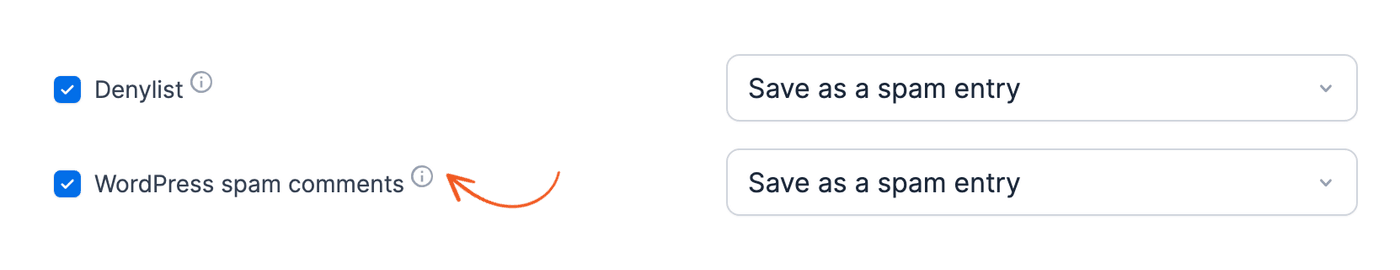
Both checks save a flagged submission as a spam entry by default. When the WordPress disallowed words check is set to Reject with an error message, the submitter sees this error message: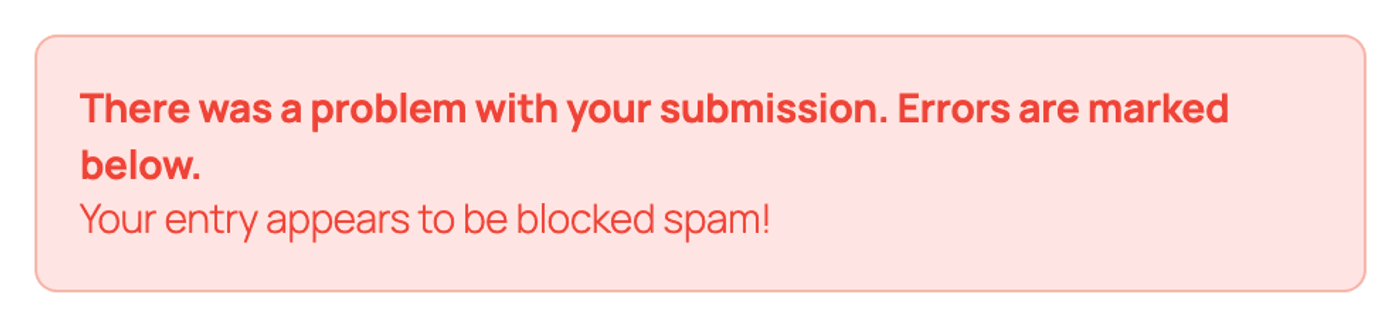
Your entry appears to be blocked spam!
To disable blacklist spam checks, use the frm_check_blacklist hook.
Block IP addresses
Use the Disallowed Comment Keys textarea in the Discussion Settings to block IP addresses. A submission from an IP address in this list is flagged as spam, and that IP address is blocked from uploading files.
To add an IP address with a snippet instead of editing the setting, filter the disallowed_keys option. WordPress reads the list one line at a time, so the snippet adds the IP address on a new line.
Block an IP address with a snippet
add_filter( 'option_disallowed_keys', function( $keys ) {
    return $keys . "\n" . '203.0.113.10';
} );
Replace 203.0.113.10 with the IP address you want to block.
If you are getting multiple file uploads from a specific IP, you can block and prevent the IP from uploading any files by adding the IP address to your disallowed comment keys.
CleanTalk
Anti-Spam by CleanTalk is a cloud-based service with a firewall that helps prevent spam bots before they get access to your website. It analyzes comments on your site and determines if it's from a visitor or a spam bot. If the comment is found to be from a spam bot, they will be blocked. You can install CleanTalk on your website.
Review spam entries
Submissions saved as spam go to the Spam tab of the entries list. Spam entries are hidden from Views and other entry lists, and their form actions don't run.
- Go to Formidable → Entries, or open a form's Entries page.
- Click the Spam tab. The number in brackets is how many spam entries there are. The Spam reason column shows which check flagged each entry, or Manual review for entries you marked as spam yourself.
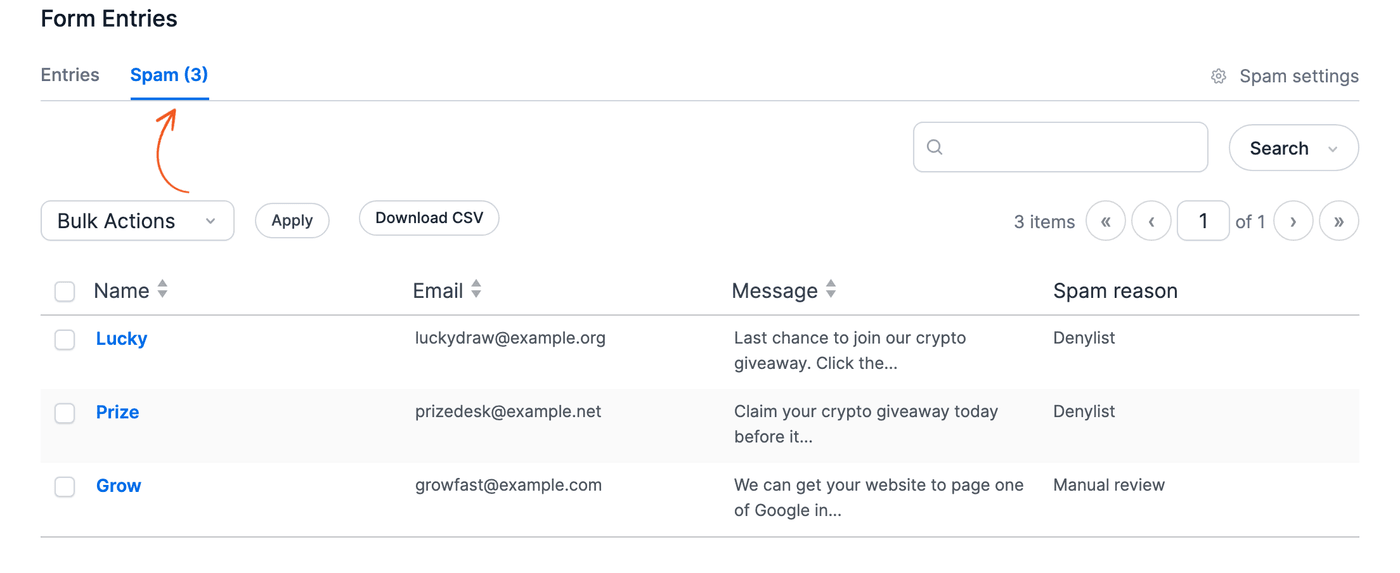
Click Spam settings on the Spam tab to go to the spam settings. When you're viewing one form's entries, it opens that form's Spam settings. Otherwise, it opens Global Settings → Captcha/Spam.
Spam entries can be viewed and deleted, but not edited or duplicated. When you open a spam entry, a notice at the top explains why it was marked as spam.
Mark an entry as not spam
When a real submission is flagged by mistake, move it back to the Entries tab.
- On the Spam tab, hover over the entry and click Not spam. The entry opens with a window where you choose the form actions to run. You can also open the entry and click Mark as Not Spam in the sidebar, or Mark as not spam in the notice.
- In the window, check the form actions you want to run now, such as an email notification. Actions with conditional logic only run when their conditions are met.
- Click Mark as not spam.
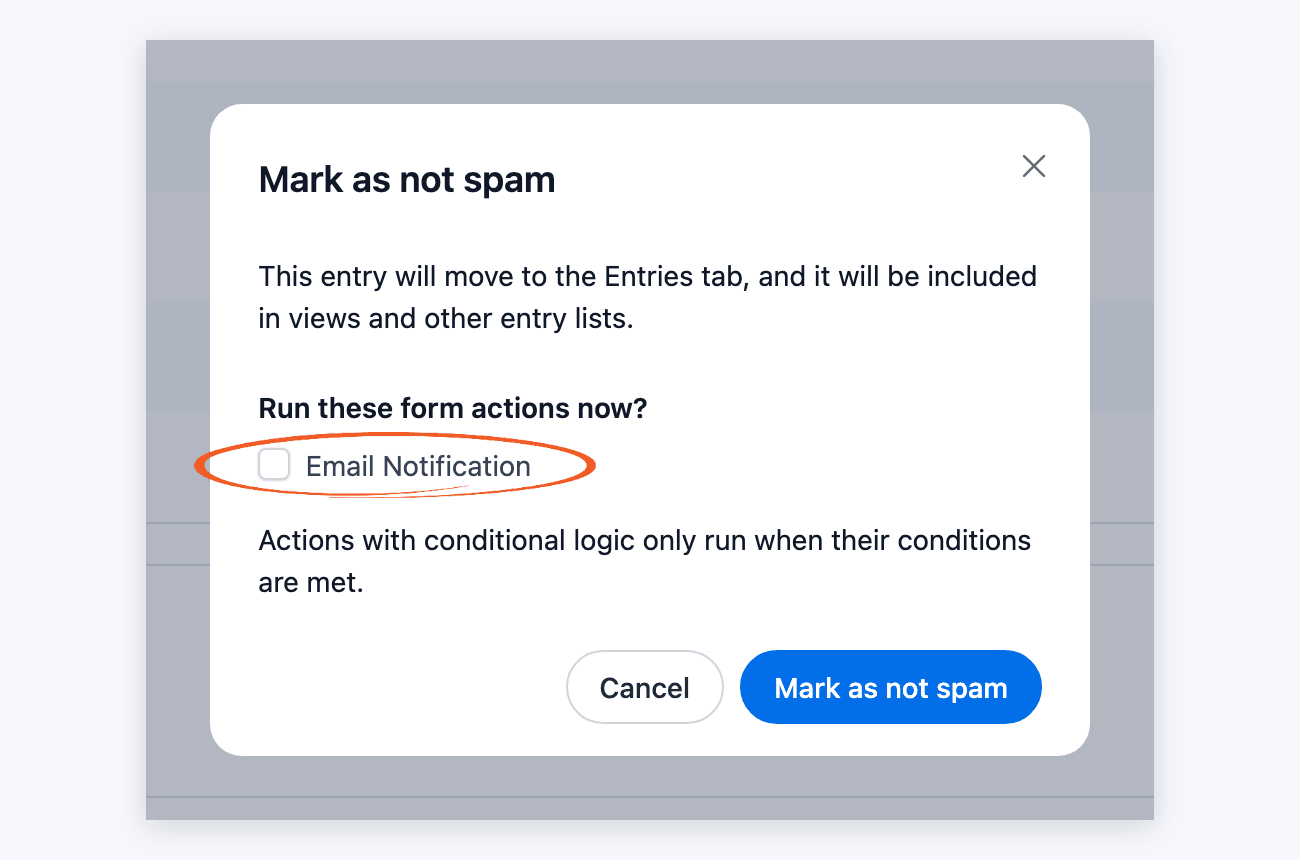
The entry moves to the Entries tab and is included in Views and other entry lists again. Payment actions and confirmation actions aren't listed, because they need the submitter's original browser session. If you marked the entry as spam yourself, its form actions already ran when it was submitted, so they won't run again.
Mark an entry as spam
To move a submitted entry to the Spam tab, hover over it on the Entries tab and click Mark as spam. You can also open the entry and click Mark as spam in the sidebar.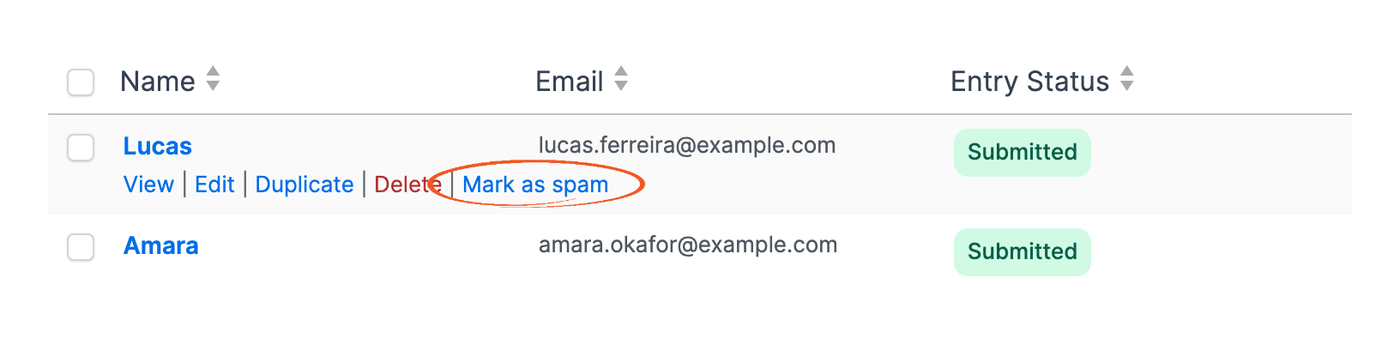
Form actions that already ran for the entry aren't reversed. Marking an entry as spam or not spam needs the same permission as deleting entries.
Delete spam entries automatically
This setting is available on the Basic, Plus, Business, and Elite licenses.
Spam entries can be deleted automatically, so the Spam tab doesn't keep growing.
- Go to Formidable → Global Settings → Captcha/Spam.
- Under Spam entries, choose an option from the Delete spam entries automatically dropdown: Never, or After 7 days, 15 days, 30 days, 60 days, or 90 days. The default is After 30 days.
- Click Update to save your changes.
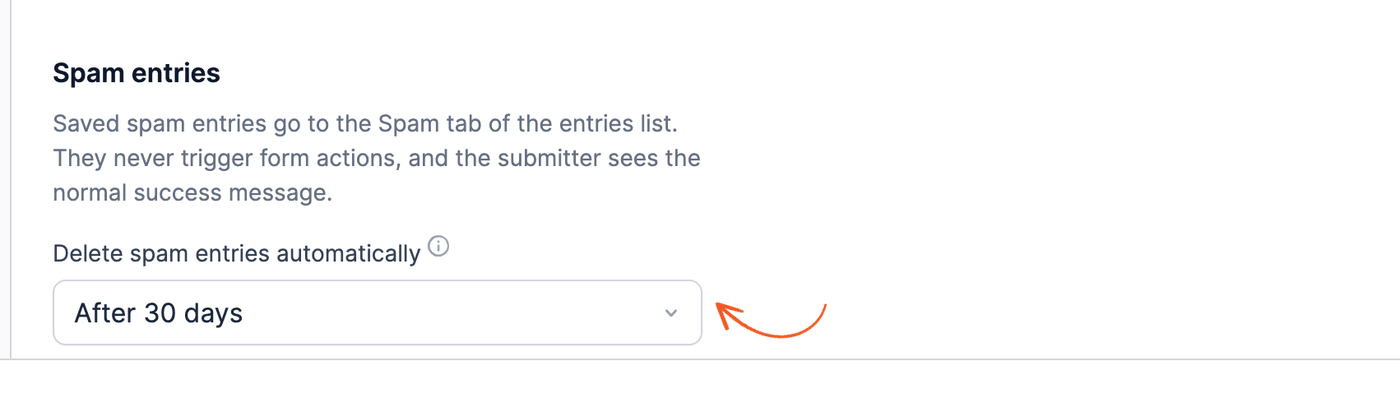
Spam entries older than the selected period are permanently deleted once a day. An entry you marked as spam yourself is counted from the date you marked it.
Troubleshooting
An entry is missing and no email was sent
If a visitor saw the success message but the entry isn't in your entries list, check the Spam tab. A spam check set to Save as a spam entry saves the submission there without running its form actions, so no email notification is sent. If the entry is real, mark it as not spam and choose the form actions to run.
Spam submissions continue
If you are still receiving spam submissions with reCAPTCHA installed, you may be seeing manual spam rather than automated. We have seen this happen occasionally on various sites. Manual spam attacks are much more difficult to prevent with automated spam protection. There are a few options available by combining multiple spam prevention options.
- Add Akismet. Since Akismet is frequently updated, there may be certain IPs, URLs, or phrases that other options may not catch.
- Check the entries for common phrases, URLs, or IPs. If you find something repeated, add it to the comment blacklist. This works well for targeted manual spam.
Your entry appears to be spam
This error message only appears for a spam check set to Reject with an error message. If you see it and have Akismet installed, follow these troubleshooting steps.
If you don't have Akismet installed, the Honeypot spam protection system is one possible source of this error message. We have seen this occasionally happen when autocomplete is enabled in the browser. It can sometimes add a value to the hidden Honeypot field, marking the entry as spam. Turn off Honeypot in the global spam checks, or set it to Save as a spam entry to save these entries for review.
Your entry appears to be blocked spam
If you see this message, the submission is being caught by a line in the comment blacklist or the denylist. That check is set to Reject with an error message. Remember that WordPress checks for word fragments, so something like "woo" also flags "woocommerce."
That file looks like spam
If you see this error message, it may be due to the Honeypot spam protection system. To fix this, go to Formidable → Global Settings → Captcha/Spam, open Customize how spam submissions are handled, and uncheck Honeypot.
Form token is invalid
This message can appear when the JavaScript token is outdated when the form is submitted. It is often caused by the cache holding onto the old page without the token.
- Best solution: Extend the time that a token is valid with the frm_form_token_check_before_today hook.
- Temporarily disable any plugins that include caching.
- Clear all browser and hosting caches.
- Investigate any external caching like Cloudflare or MaxCDN.
This page isn't loading JavaScript properly
This error message is displayed when the antispam token fails to validate because no token is sent. This means there is a JavaScript issue on the page, which is usually related to the theme, custom code, or another plugin. See how to fix it.
For a quick fix, turn off the antispam token. To do so, go to your form Settings → Spam, and uncheck the box to Check entries for spam using JavaScript.
Host or security scanner flags a Formidable file as malware
If your host or a security scanner flags the file denylist/splorp-wp-comment.txt inside the Formidable Forms plugin folder (often reported as malware or a phishing threat), this is a false positive. That file is part of Formidable's built-in denylist, used to check form entries for spam words. It doesn't execute code and isn't a security risk.
If your site gets quarantined over this, share this explanation with your host and ask them to whitelist the file and restore your site. If a security plugin keeps re-flagging it, add the file to that plugin's exclusion list.
Related developer hooks
- To turn off Honeypot on one or all forms, use the frm_run_honeypot hook.
- To manually flag the submission of a form as honeypot spam, use the frm_process_honeypot hook.
- To remove the spam bot error when there is no IP, use the frm_validate_entry hook.
- To extend the valid token times before today, use the frm_form_token_check_before_today hook.
- To extend the valid token times after today, use the frm_form_token_check_after_today hook.
- To filter the stopforumspam API based URL, use the frm_stopforumspam_api_url hook.
- To filter the request data sent to the stopforumspam API, use the frm_stopforumspam_request_data hook.
